Nikkei Inc. has disclosed its third cybersecurity incident in about a month, saying a breach exposed 1.83 million personal information records and renewed questions over how securely the Japanese media giant protects employee, partner and customer data.
Nikkei reports third cyber breach in a month
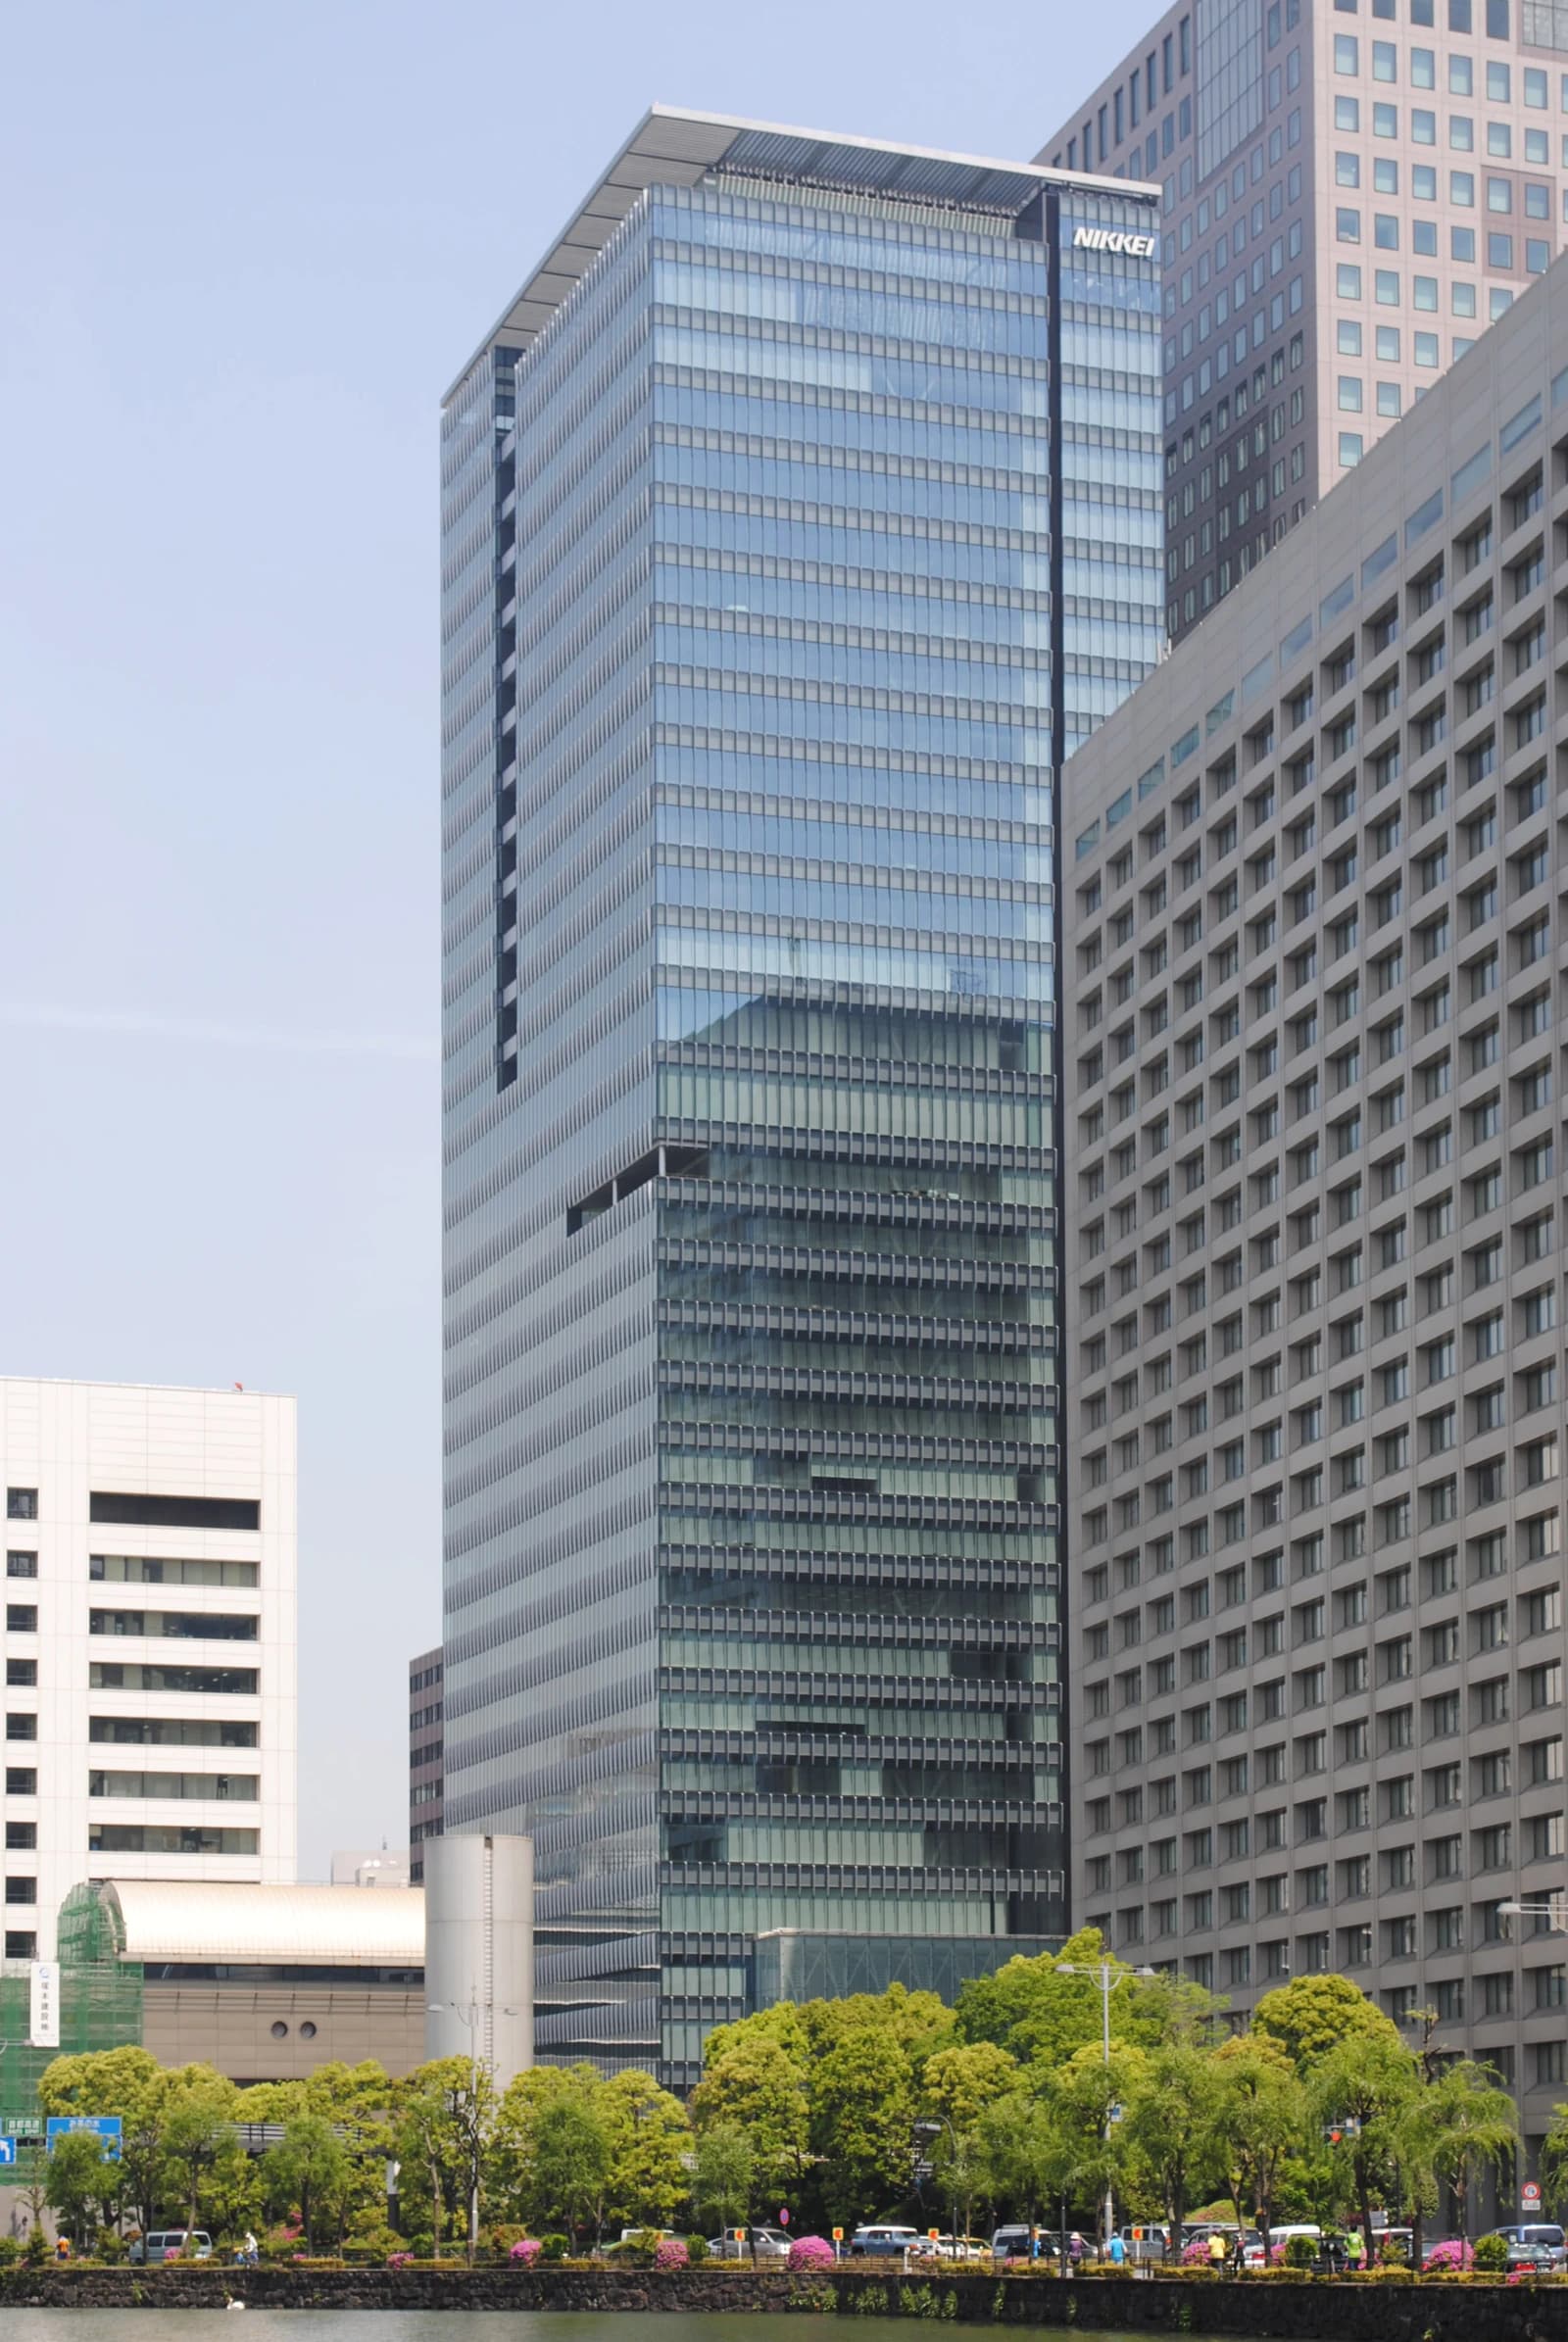
The breach matters because Nikkei sits at the center of Japan’s business-information ecosystem and owns the Financial Times, making any lapse in its internal controls a reputational and operational issue well beyond a routine IT incident. The company said most of the exposed records contained no identifying information, but 150,000 included personal details such as names, email addresses, phone numbers and birth dates.
Sentiment Indicators
Email addresses appeared in 120,000 records, while Nikkei said no credit card data was exposed. It also said there was no evidence as of Oct. 16 that the information had been misused or leaked online, and that no services were disrupted.
According to Nikkei’s notice, attackers used stolen credentials to reach a development system in the early hours of Oct. 7 and accessed personal information stored in the cloud. The company revoked the compromised credentials and notified Japan’s Personal Information Protection Commission on Oct. 11, but said it is still investigating the full scope of the incident.
The latest disclosure follows two earlier breaches Nikkei announced this month: one tied to a compromised Google Workspace account in late July and another involving a hijacked Microsoft 365 account used to send spear-phishing emails to staff in September. The repeated intrusions suggest attackers have been able to exploit valid credentials rather than break through perimeter defenses, a pattern that can be harder and costlier for companies to contain.
For investors, the immediate issue is not direct financial damage but the cumulative hit to trust, compliance costs and management bandwidth at a company whose business depends on safeguarding sensitive information and maintaining credibility with corporate clients. The incident also underscores a broader cybersecurity risk for large enterprises increasingly storing data in the cloud and relying on identity-based access controls.
Nikkei said affected individuals will be notified and that it will strengthen security measures, while the investigation continues. The next catalyst is whether regulators, partners or customers demand additional disclosures or controls after the third breach in such a short period.
| Entity | Gains | Losses |
|---|---|---|
| Attackers | ▲Access to stored data | ▼Exposure risk if traced |
| Nikkei | ▲Chance to tighten controls | ▼Reputation, trust, compliance costs |
| Customers and staff | ▲Notification and monitoring | ▼Privacy and security risk |
| Competitors | ▲Relative trust advantage | ▼Industry-wide scrutiny |